New Free whitepaper: the Kraljic Matrix applied to 20 real EPC procurement categories - get the PDF.
Security & Compliance

Security controls built into every workflow.

Role-based multidimensional access control, multi-factor authentication, encryption and full audit trails - by default, on every module, not as a premium add-on. procurEngine is ISO 27001 and ISO 27701 certified, independently audited.
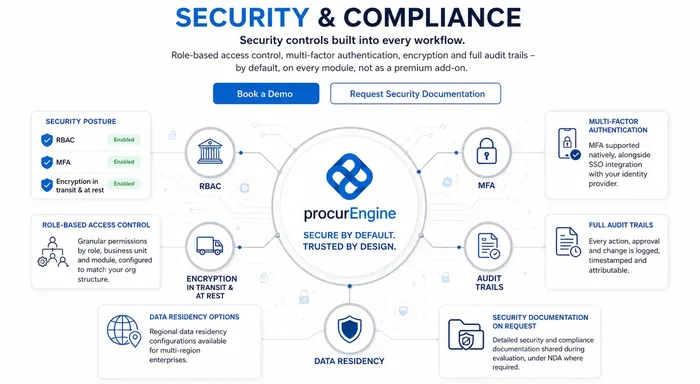
Security & Compliance: role-based access control, multi-factor authentication, encryption, audit trails and data residency controls built into every module
Security foundations

What's built in, by default.

Role-based Multidimensional access control

Granular permissions by role, business unit and module, configured to match your org structure.

Multi-factor authentication

MFA supported natively, alongside SSO integration with your identity provider.

Full audit trails

Every action, approval and change is logged, timestamped and attributable. Retention and export options are covered in the security pack.

Encryption in transit & at rest

Encrypted in transit and at rest throughout the platform. Protocols, ciphers and key management are detailed in the security pack.

Data residency

Residency for your deployment is confirmed during evaluation and set out in your contract.

Security documentation on request

Detailed security and compliance documentation shared during evaluation, under NDA where required.

Security pack

What your security review will get, and when.

Specifics are shared with evaluation teams under NDA rather than published, so that what governs your deployment is the detail in your agreement. The pack covers the standard questionnaire ground:

  • Encryption - protocols and ciphers in transit and at rest, and how keys are managed and rotated.
  • Hosting and data residency - where your deployment runs, and what is configurable.
  • Audit logging - what is captured, how long it is retained, and how you export it.
  • Sub-processors - who else processes your data, and for what.
  • Incident response - the runbook, escalation contacts and notification commitments, which are set contractually.
  • Access control - role and business-unit permissions, MFA and SSO against your identity provider.

Incident response, access control and the rest of the above sit within our ISO/IEC 27001:2022 certified ISMS and are independently audited as part of that certification - see our certifications.

Certification status

What we hold, and what is in progress.

Stated plainly, so an evaluation team can establish our posture from this page rather than waiting on a sales conversation.

ISO/IEC 27001:2022 Certified

Information Security Management System (ISMS), certified by Intertek Certification Limited, a UKAS-accredited certification body. Scope: the ISMS at AgileApt Solutions Private Limited (Noida, India), applying to the application development, maintenance and support of procurEngine (SaaS), supported by IT, HR, Admin, Legal, Sales and Marketing. Certified since June 2025 and valid to June 2028, subject to Intertek's ongoing surveillance.

ISO/IEC 27701:2019 Certified

Privacy Information Management System (PIMS), certified by Intertek as an extension to our ISO/IEC 27001:2022 certification and valid in combination with it. Same entity and product scope, with AgileApt Solutions acting as both PII Controller and PII Processor. Certified since June 2025 and valid to June 2028.

SOC 2 In progress

A SOC 2 examination is underway. Report type and target completion date are shared with evaluation teams on request.

GDPR & DPDP Programme underway

Neither is a certification scheme, so no vendor can hold a certificate against them. Our ISO 27701-certified PIMS underpins our GDPR and DPDP compliance programmes, which are ongoing.

Both ISO certifications are described in full on our certifications page. Certificates, certificate numbers and audit documentation are shared on request during evaluation, under NDA where required, and Intertek certificate validity can be confirmed directly with Intertek.

FAQ

Security questions we hear often.

How is access to procurEngine controlled?
Role-based multidimensional access control (RBAC) and multi-factor authentication (MFA) are supported natively, alongside SSO integration with your enterprise identity provider.
Is data encrypted?
Yes, in transit and at rest throughout the platform. The specific protocols, ciphers and key management approach are set out in our security pack, shared with evaluation teams under NDA rather than published.
What compliance certifications does procurEngine hold?
procurEngine holds ISO/IEC 27001:2022 for information security management, extended by ISO/IEC 27701:2019 for privacy information management. Both are certified by Intertek Certification Limited, a UKAS-accredited certification body, and cover the application development, maintenance and support of procurEngine (SaaS) at AgileApt Solutions Private Limited, Noida, India. Certified since June 2025 and valid to June 2028. A SOC 2 examination is in progress. Both certifications are described in full on our certifications page, and certificates and audit documentation are shared on request during evaluation.
Is procurEngine GDPR and DPDP compliant?
Neither the GDPR nor India's DPDP Act is a certification scheme, so no vendor can hold a GDPR or DPDP certificate. Our ISO 27701-certified Privacy Information Management System - the privacy extension to ISO 27001 - underpins our GDPR and DPDP compliance programmes, which are ongoing. Website data handling is set out in our privacy policy; product data processing is governed by a Data Processing Agreement entered into with each customer.
Where is my data stored?
Hosting region and data residency are confirmed for your deployment during evaluation and set out in your contract, rather than published here. Residency is covered in the security pack.
How long are audit logs retained, and can we export them?
Every action, approval and change is logged, timestamped and attributable. Retention periods and export options are covered in the security pack, shared under NDA during evaluation.
Who are procurEngine's sub-processors?
The sub-processor list is provided in the security pack during evaluation. Product data processing is governed by the Data Processing Agreement in your contract, which is separate from this website's privacy policy.
What is procurEngine's incident response process?
Incident response sits within our ISO/IEC 27001:2022 certified ISMS and is independently audited as part of that certification. The runbook, escalation contacts and notification commitments are set contractually and shared in the security pack, so the timeline in your agreement is the one that governs.

Request our security documentation.

Talk to us for detailed security and compliance documentation as part of your evaluation.